System architect, implementer and operator.
AI operations & exact action authorization
Nexus Agent Operations
Useful agents. Bounded authority.
A human-governed agent platform for real email, inbox and research workflows. Generated work stays separate from permission to act, while approvals, audit trails and shutdown controls surround every external operation.
Working platform · Provider evidence · Auditable controls
Project video · 6:24
Nexus: human-governed agent operations
A walkthrough of Nexus controls for review, authorization, bounded dispatch and operational recovery.
Click the picture to play. Full screen and volume are available in the controls.
Open the video file ↗LiveGmail delivery and inbox workflowsTypedoperation registry and plan compilerHumanapproval-bound external actionsPrivateimplementation; public account below
Typed operations, durable queues and human review surfaces across research, email and external integrations.
Planning, review, exact dispatch authority, provider outcome and audit evidence became separate system states.
Private implementation screens, real Gmail operation and bounded provider-validation records.
01 / The difficult question
How can an agent act without becoming the authority?
Agent systems become operationally risky when a model can blur the line between proposing an action and authorizing it. Nexus treats that boundary as a system invariant rather than a prompt instruction.
The difficult question was how to retain useful research, planning and drafting while making every state-changing operation pass through typed validation, identity checks and a human-bound permit—and then reconcile what actually happened at the provider.
02 / Brian's contribution
Turn policy into executable boundaries.
Brian built the typed operation registry and plan compiler exposed through an MCP interface, along with scoped service keys, role checks and kill switches. Approved content is bound to immutable snapshots, content hashes and exact dispatch permits.
He also implemented append-only audit events and durable Neo4j/Aura queues with atomic claims, idempotency, retries and reconciliation. The platform now supports real Gmail outreach and inbox workflows, Serper-backed research, a bounded Buffer lifecycle, live graph-schema work and controlled affiliate-tool validation.
03 / How the system works
01Research & draft
Agents prepare evidence and candidate content.
→02Compile & validate
Typed operations reject unknown or malformed intent.
→03Review & bind
A person approves an immutable content snapshot.
→04Permit & audit
Only the exact approved operation may dispatch.
The model can propose the plan, but it cannot mint the permit that makes the plan operational.
04 / Failure-aware operations
Every transition has an owner and a recoverable state.
Queues use atomic claims and idempotent operations so a retry does not silently duplicate work. Reconciliation makes stalled or ambiguous operations visible rather than treating absence of an exception as success.
Kill switches and scoped identities sit outside the model layer. The operational design assumes models can fail, services can time out and reviewers can reject a draft.
Permit lifecycle
Authority is narrowed at every transition.
Draft→Compiled→Reviewed→Permitted→Audited
unknown operation → rejectcontent changed → invalidatedispatch ambiguous → reconcile
From drafting system to operational lifecycle
Nexus has delivered real email through Gmail, ingested inbox replies, supported response drafting and exercised live research, social, cloud and graph integrations under human control.
Provider tests with explicit boundaries
Controlled tests exercised Buffer, AWS and Tapfiliate paths without presenting those checks as unrestricted production operation.
Private implementation evidence
Control surfaces, shown.
The hero establishes the review model. This second sanitized capture shows active work, timing, safety controls and shutdown status.
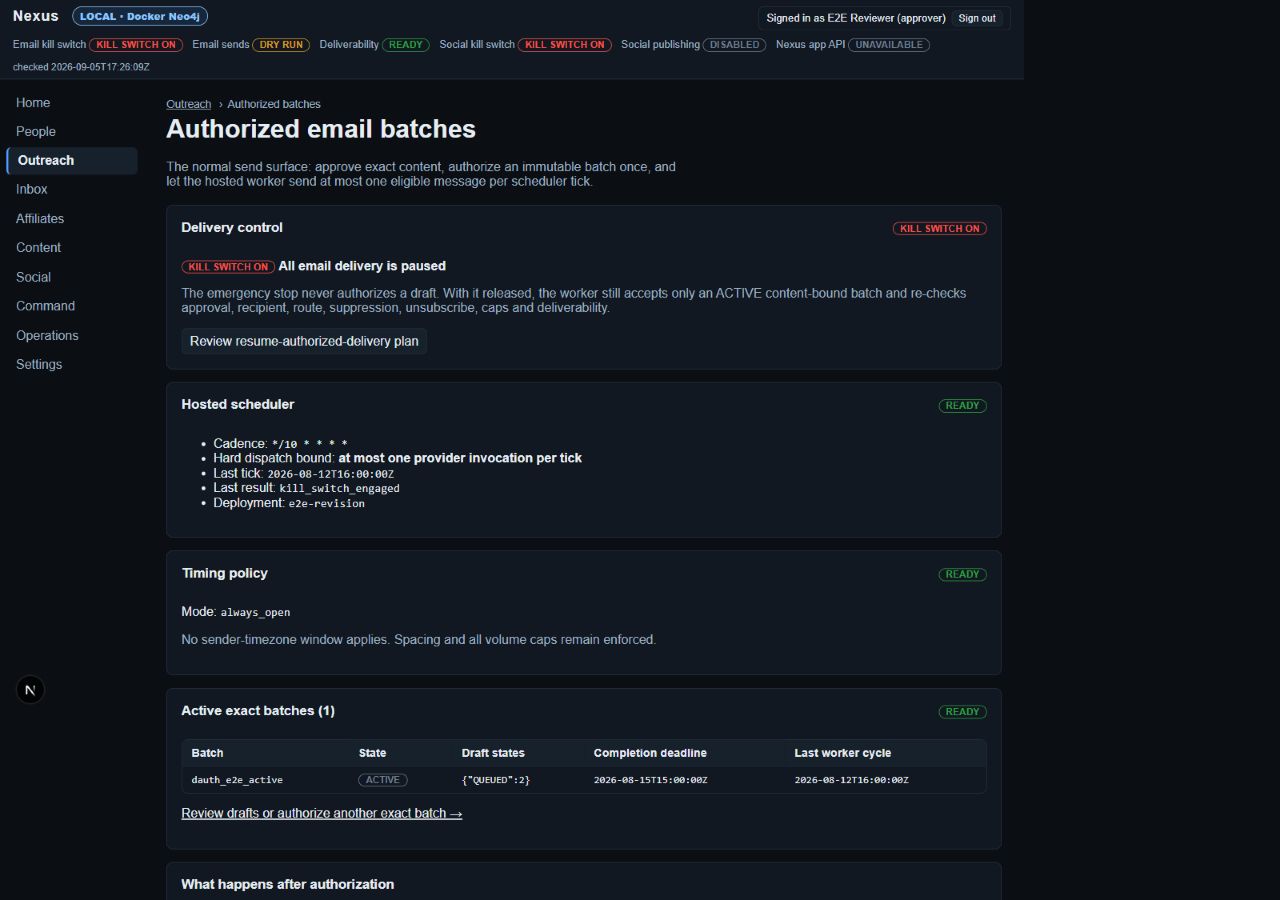
The operations view makes active work, timing, safety controls and shutdown status visible in one place.
Open full-size view ↗Scope & limitations
Operational evidence, not unrestricted automation or certification.
The Nexus implementation is private. The selected sanitized interface captures demonstrate review and control surfaces, but they do not provide independent inspection of the codebase or a live deployment.
Gmail is the current outbound route. AWS infrastructure was validated, but SES is not the active production email service and its production-access request was rejected. Serper is an integrated fresh-research capability; the repository does not establish equally strong evidence of routine production use.
The Buffer exercise was a controlled provider interaction, not a public social-media publication. General automated production publishing and general affiliate operations remain gated. No claim is made that the architecture eliminates every security risk or constitutes a security certification.
Inspect the evidence
Selected interface evidence and public role context.
Useful when
Your team is automating real workflows where generated work, approval, exact action authority and provider outcomes must remain separate.
Explore governed-agent validation →